The Rising Threat of Prompt Injection in AI Coding Agents
Attackers are embedding malicious instructions inside repository files that AI coding agents process silently. Traditional endpoint security is blind to this vector — and the consequences can be catastrophic.
Read Article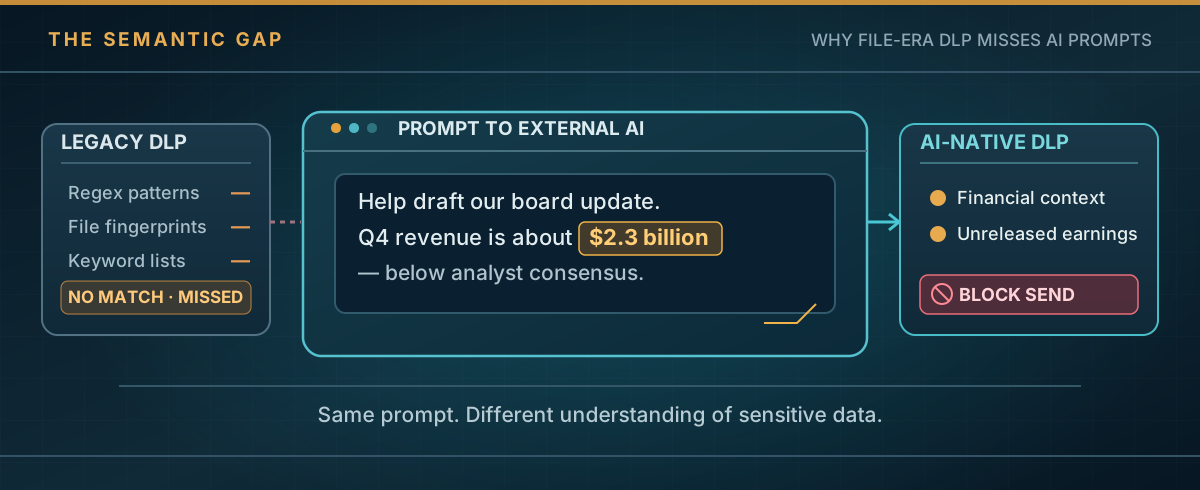
Why Traditional DLP Fails in the Age of Generative AI
Legacy DLP was built for structured data and regex patterns. Freeform LLM prompts break every assumption it was designed around.
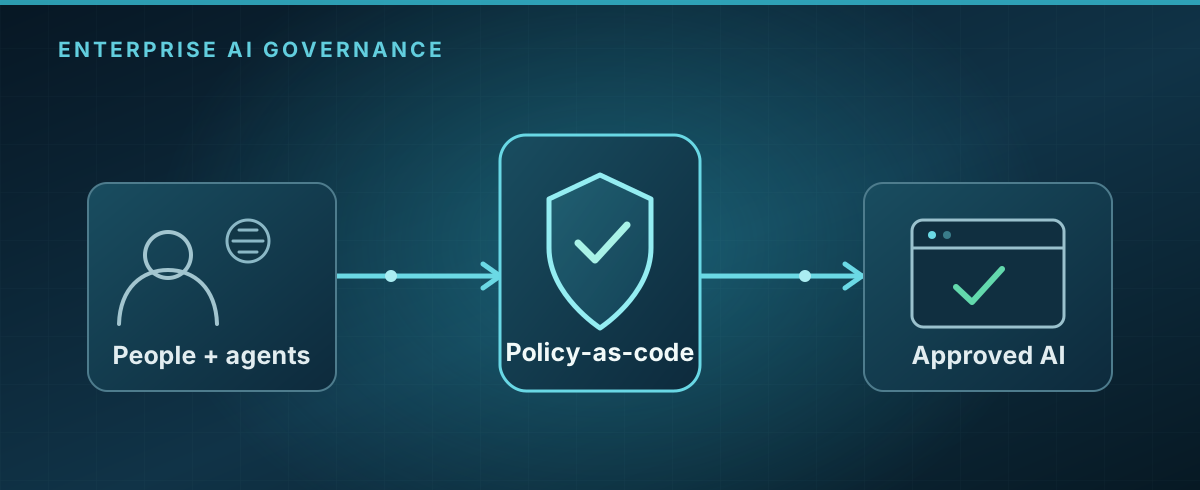
AI Security in 2026: The CISO Playbook for Enterprise AI Adoption
The five control domains every CISO is deploying right now, and the three maturity stages separating visibility from true governance.
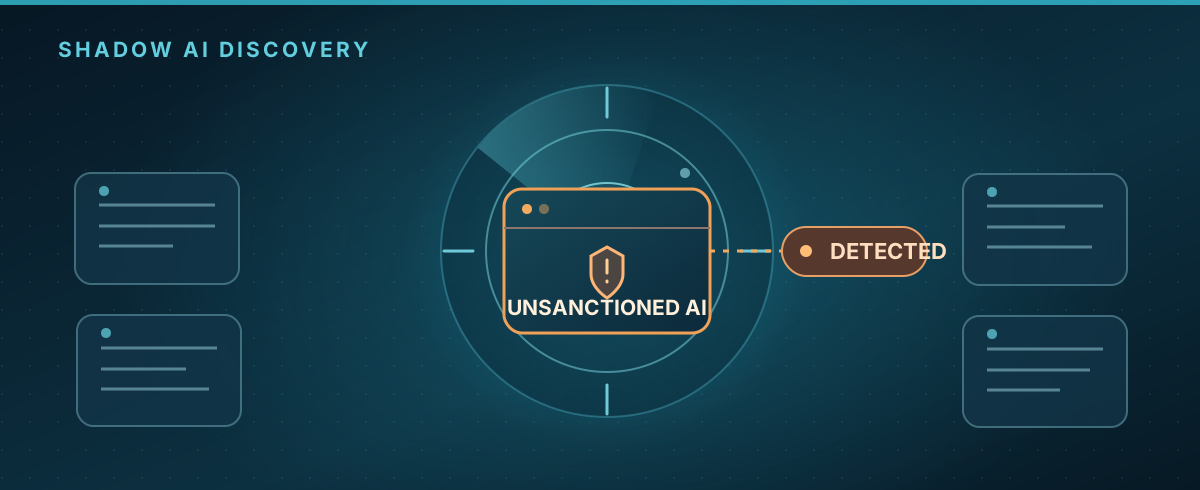
Shadow AI: The Fastest-Growing Attack Surface You're Not Monitoring
Shadow AI is worse than shadow IT — data exits in prompts, not files. Here's the methodology for discovering and governing unsanctioned AI tool usage.
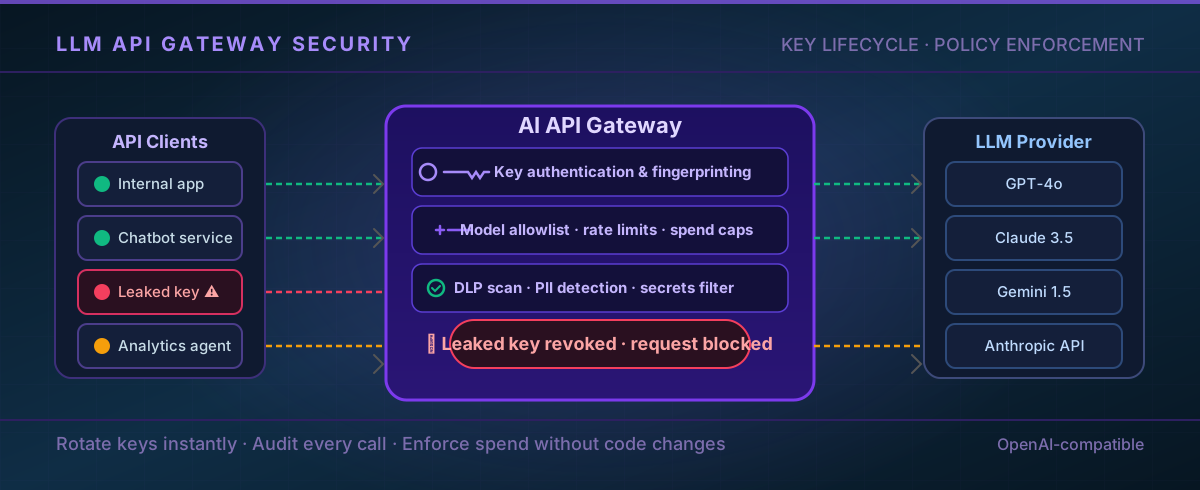
Securing the LLM API Layer: Why Your AI Gateway Matters
A single leaked OpenAI API key can cost six figures in hours. The gateway is your security boundary — but only if it's built for AI-era threats.
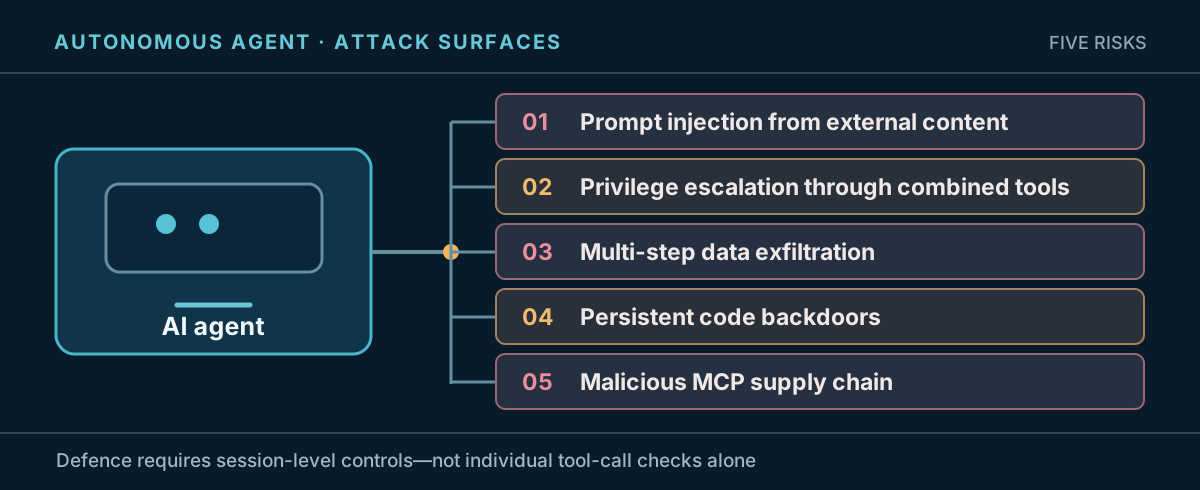
The Five Security Risks of Autonomous AI Agents
From prompt injection via environment files to supply chain attacks via malicious MCP servers — the threat landscape for AI agents is broader than most teams realise.
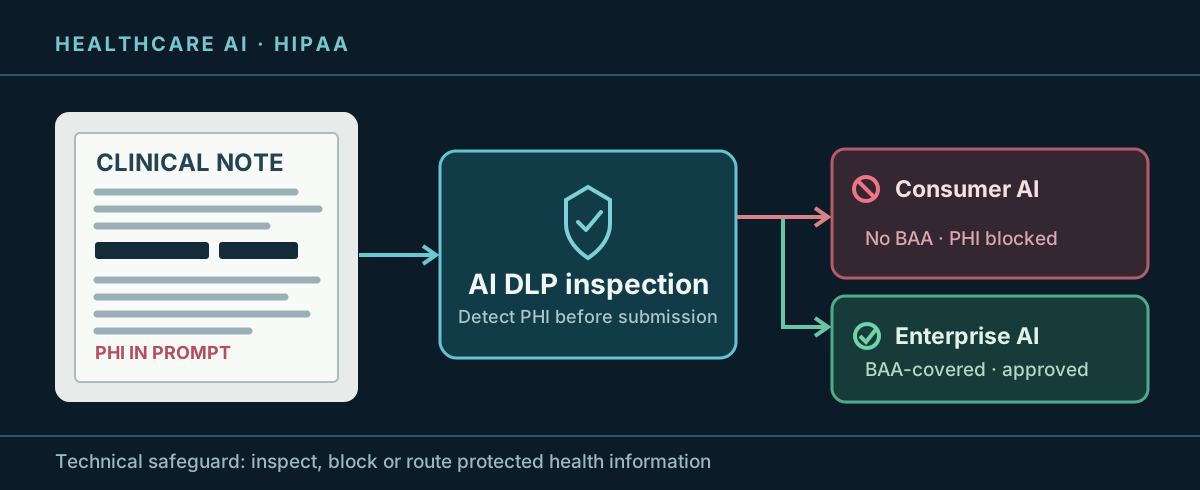
AI and HIPAA: What Every Healthcare CIO Needs to Know
Clinical staff are using ChatGPT for patient documentation without a BAA. The OCR enforcement clock is ticking — here's the five-step compliance programme.
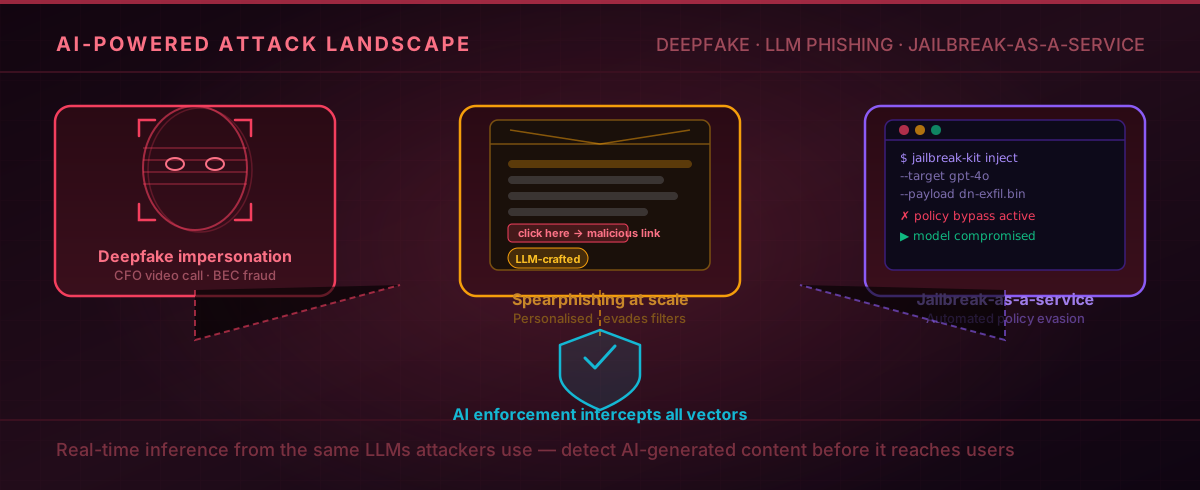
AI-Powered Attacks: How Attackers Are Using the Same Tools You Are
LLM-crafted spearphishing, deepfake BEC fraud, and jailbreak-as-a-service ecosystems — the attacker advantage is narrowing, but only with real-time enforcement.
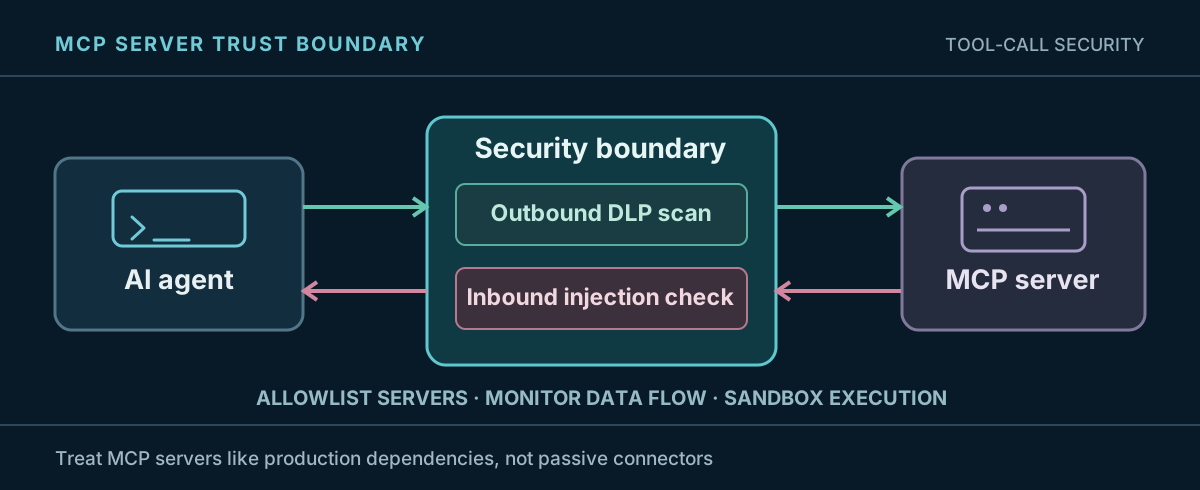
MCP Security: The New Attack Surface Nobody Is Talking About
Model Context Protocol gives AI agents powerful capabilities. It also creates a direct code execution path from untrusted AI input — and the security industry has barely noticed.
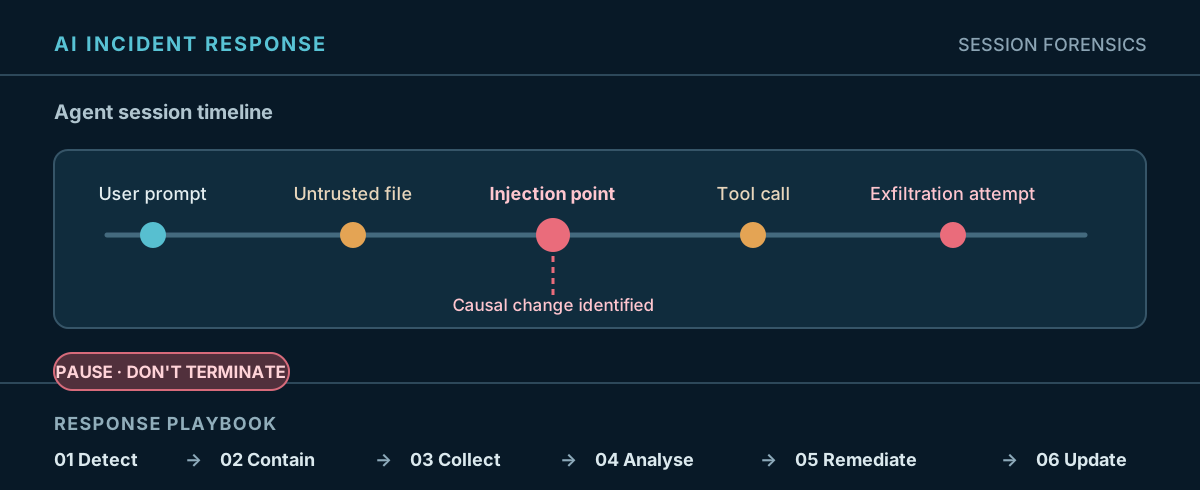
AI Security Incident Response: How to Investigate an Agent Compromise
Traditional IR playbooks don't apply to AI incidents. No default logs, no memory forensics for LLM context — here's the six-step AI IR process.